Remote support, monitoring and security for every device — in one console.
Salus is INconnet’s own RMM and security platform. Multi-client and modular, it supports, patches and protects your devices and networks across countries, scans every site for vulnerabilities and rates every device from A to E.
One platform we own and run — not a stack of resold tools.
Because Salus is built and operated by INconnet, we control its features, security and roadmap. Support, monitoring, security and tickets live in one place, with one accountable team.
Every device on every network, rated from A to E.
Salus scans each site for devices and vulnerabilities, protects endpoints with detection and response (EDR) capabilities and gives every device a trust rating — laptops, servers, POS, printers, cameras and routers. You see the risk of each site and of the whole region in one score, like the security ratings used to assess vendors.
- Discovery of everything connected to each site network
- Vulnerability and open-port scanning
- Managed EDR with incident response and quarantine
- A–E rating per device, per site and per country
- Prioritised remediation and month-over-month trend
This is how we see your estate.
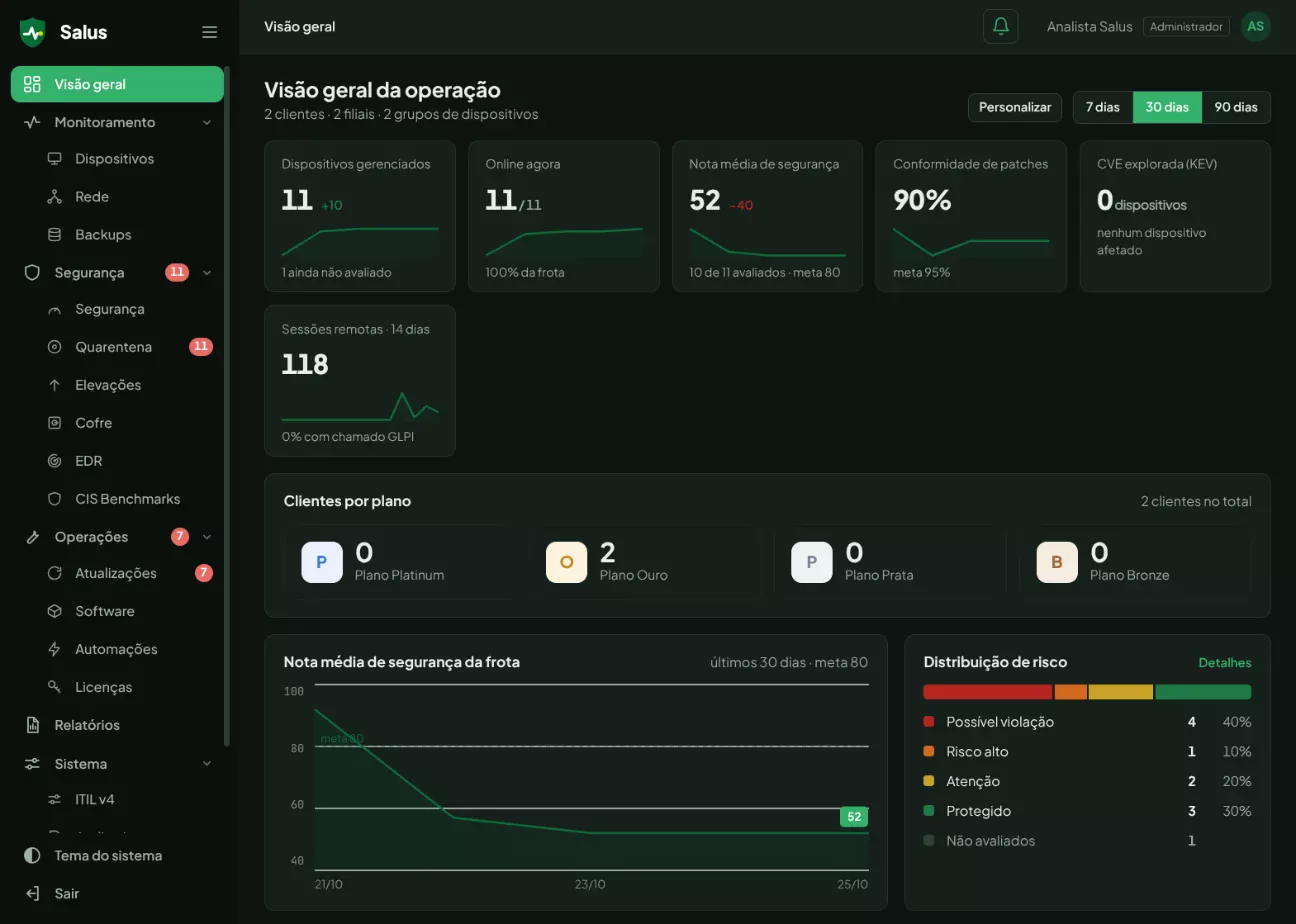
Security posture for every device and a network rating for every site, updated continuously.
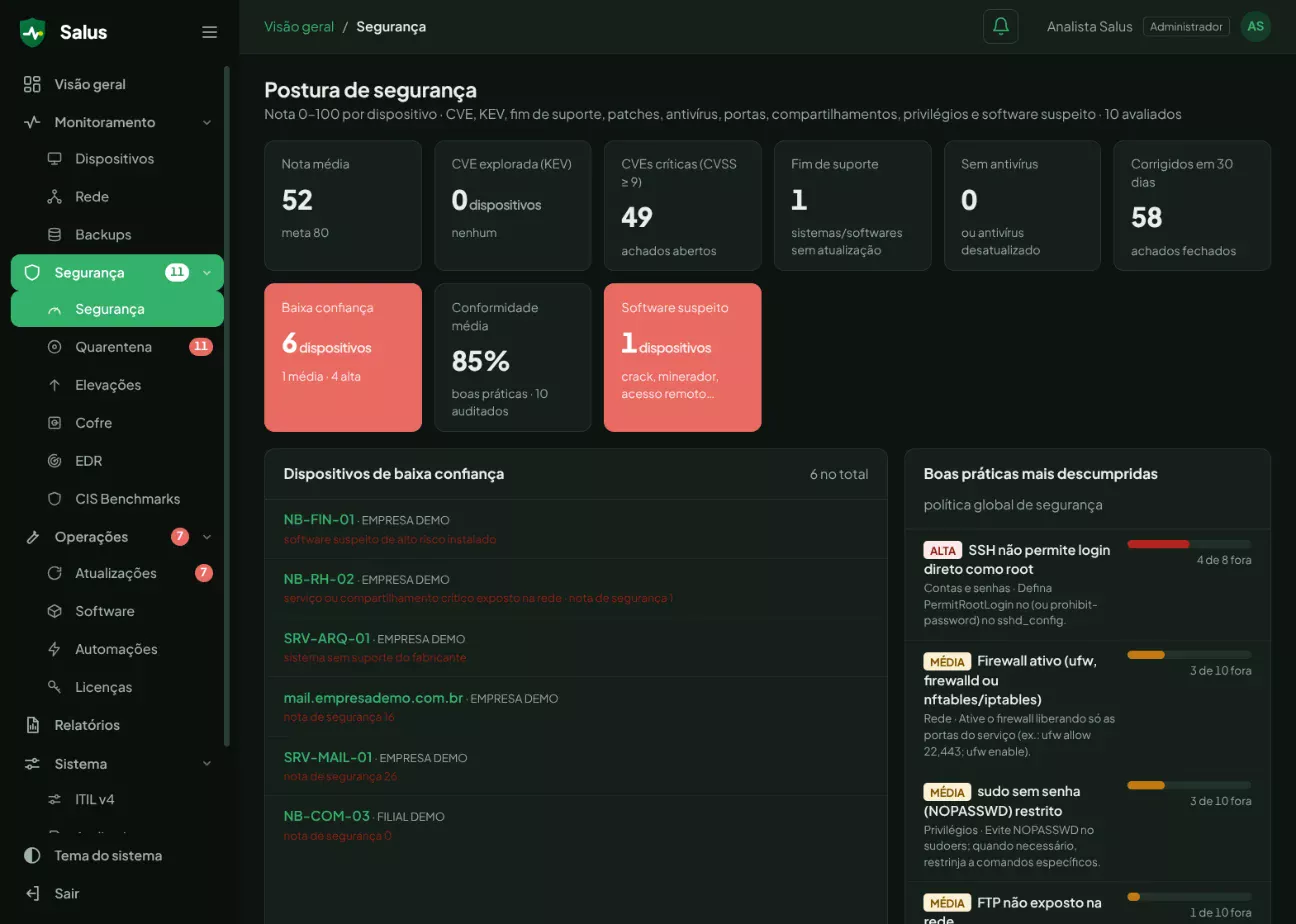
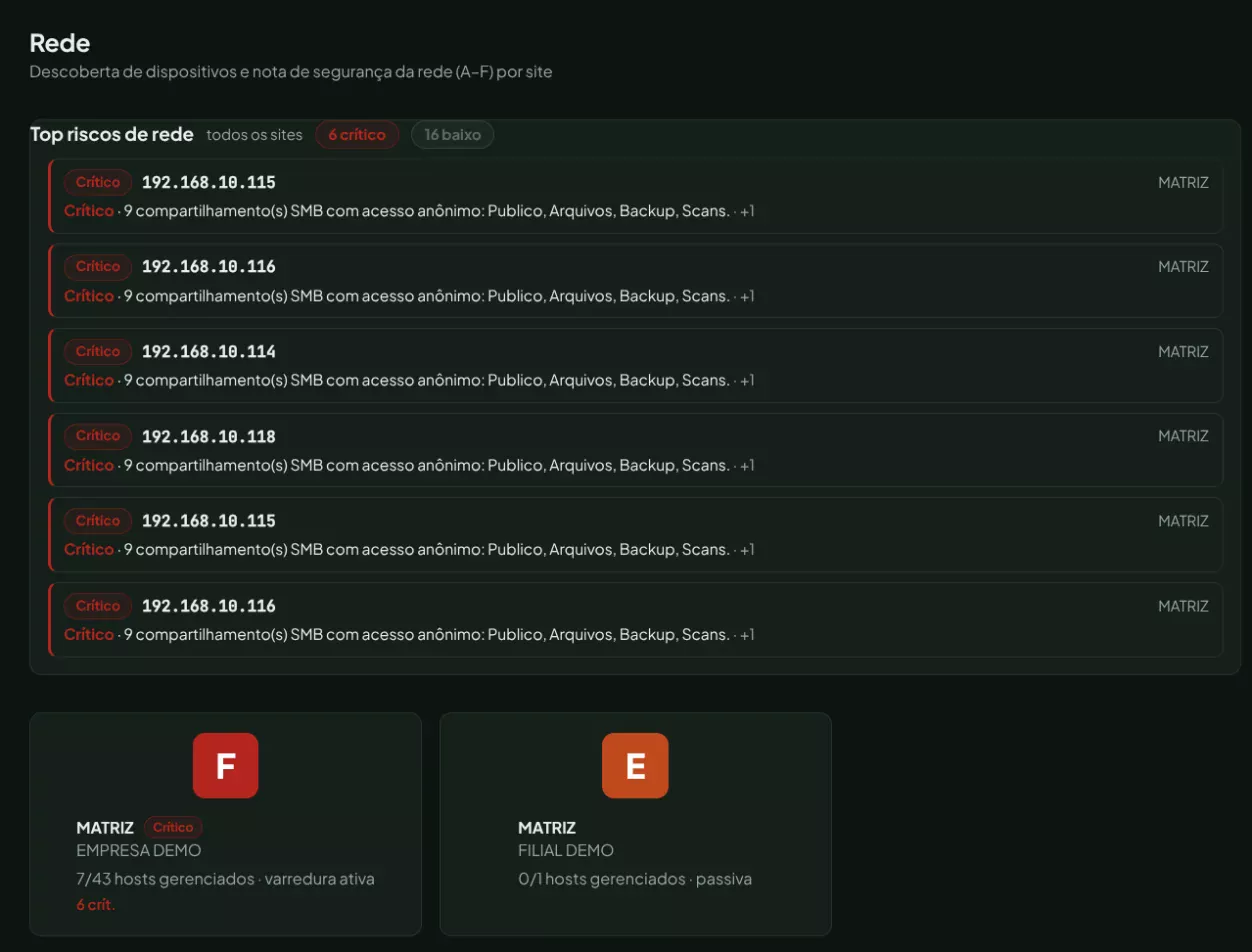
Real Salus screens (Portuguese interface). Company, device and address names have been replaced.
Eight capabilities, one console.
Remote access
Desktop, terminal and files through token-based sessions linked to a ticket.
- No exposed credentials
- Time logged per ticket
Inventory & monitoring
Live inventory by country, site and user.
- CPU, memory, disk and network
- Uptime and availability
Endpoint security
Active protection on every device.
- Managed EDR / antivirus (Defender or third-party)
- Hardening: USB, DNS, AppLocker
Network & vulnerabilities
Discovery and active scanning of every site.
- Vulnerability detection
- A–E rating for endpoints and network assets
Operations & patching
Routine work done automatically.
- Windows Update and third-party apps
- Bulk scripts and automations
Privileged access & vault
Fewer shared credentials, less risk.
- Password vault
- LAPS / PEDM, incident response and quarantine
ITIL & reporting
Wired into the service desk and your monthly report.
- Automatic tickets
- Executive and maturity reports, licence management
Multi-client governance
Built for multi-country, multi-site operations.
- Clients, sites and tiers
- RBAC by team; full audit trail
Defence in layers, from sign-in to endpoint.
A remote management tool is a door into your environment, so Salus is secure by design. Our processes use ISO/IEC 27001, ISO 9001, NIST CSF 2.0 and CIS Controls v8 as reference frameworks, with every improvement cycle mapped to the relevant control.
Processes aligned with these frameworks; not a formal certification.
Request the compliance pack- 01Sign-in
Microsoft Entra single sign-on with MFA. No local passwords, no self-registration.
- 02Authorization
Role-based access by team, client and site. Least privilege by default.
- 03Session
Remote sessions use short-lived tokens tied to a ticket. No credentials exposed.
- 04Audit
Who accessed which device, when and why — full audit trail, available on request.
- 05Endpoint
EDR, hardening, vulnerability scanning and an A–E rating on every device.
Bronze to Platinum — Salus grows with each client.
Every capability is a function assigned to one or more tiers and switched on or off per client, any time, without reinstalling.
| Bronze | Silver | Gold | Platinum | |
|---|---|---|---|---|
| Remote access (desktop, terminal, files) | ✓ | ✓ | ✓ | ✓ |
| Patching (Windows Update + third-party apps) | ✓ | ✓ | ✓ | ✓ |
| Automatic tickets (ITSM integration) | ✓ | ✓ | ✓ | ✓ |
| Executive reports | — | ✓ | ✓ | ✓ |
| Backup monitoring | — | ✓ | ✓ | ✓ |
| Automations & bulk scripts | — | ✓ | ✓ | ✓ |
| Licence management | — | ✓ | ✓ | ✓ |
| Active network scanning & A–E rating | — | ✓ | ✓ | ✓ |
| Hardening | — | ✓ | ✓ | ✓ |
| Live tools (services, processes, registry) | — | — | ✓ | ✓ |
| Incident response & quarantine | — | — | ✓ | ✓ |
| Privileged access (LAPS / PEDM) | — | — | ✓ | ✓ |
| Password vault | — | — | ✓ | ✓ |
| Managed EDR / antivirus | — | — | ✓ | ✓ |
| SIEM (syslog + correlation) | — | — | — | Roadmap |
| Security connectors (Cisco, Palo Alto, FortiGate, Aruba, F5) | — | — | — | Roadmap |
| Asset & availability monitoring (SNMP / ICMP) | — | — | — | Roadmap |
Where Salus is going.
Towards a full RMM with SIEM and security integrations in the premium tier — keeping the same modular model.
SIEM / syslog
RFC 5424/3164 over UDP, TCP or TLS; normalisation, correlation rules, alerts, dashboards and case lifecycle.
Security connectors
Cisco, Palo Alto, FortiGate, Aruba and F5 events via syslog and vendor APIs, in the Salus SIEM.
Asset monitoring
SNMP / ICMP, maps and thresholds — security and availability in one view.
Granular access & critical-device secrets
Rights per client and site (view, manage, remote) and a second secret before accessing sensitive machines.
Does Salus replace our MDM?
No. It complements Intune, Jamf or Workspace ONE with monitoring, remote support, security and field integration.
Does it replace our antivirus or EDR?
In Gold and Platinum we manage Microsoft Defender or your existing third-party EDR, including response and quarantine.
Who can access our devices?
Only authorised INconnet engineers, via Microsoft Entra SSO with MFA, through token-based sessions tied to a ticket, with a full audit trail.
Where is the data hosted?
On infrastructure operated by INconnet under our security policies. Details are in the compliance pack.
Can our team access Salus?
Yes, with role-based access for your IT, security, finance and procurement teams.
Can we change tiers?
Yes, per client and at any time — functions are switched on or off without reinstalling agents.